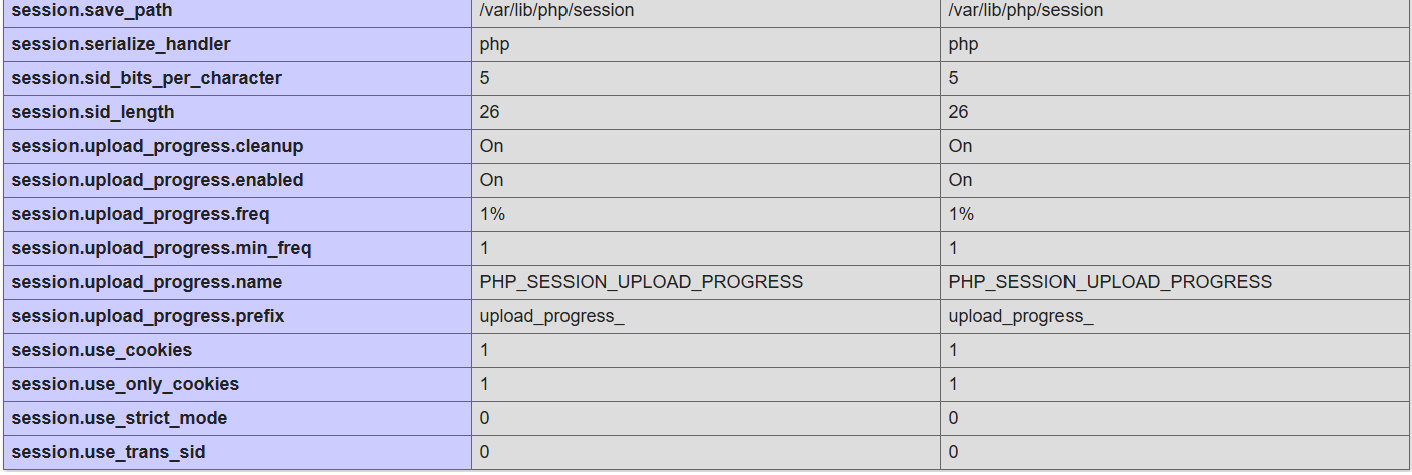
phpinfo()
This has no reason to be presented to a potential hacker. I did have a PHP script that called it for my own debugging but I renamed the phpinfo() call so that it would not reveal the internals.
In light of the PHP flaw that came to light late October 2026, PHP.net issued mitigations to curb a potential Remote Code Execution (RCE)
PHP.net had on their home page, October 2026:
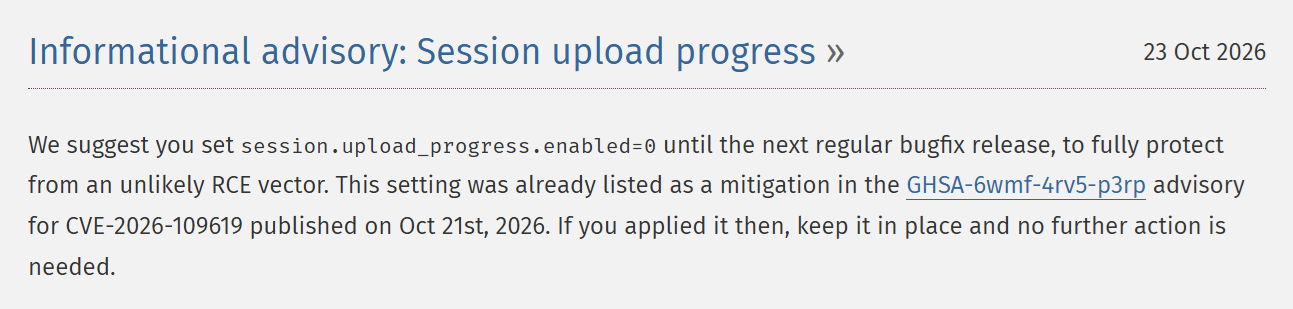
They go on to say to leave this setting as it was set as a consequence of CVE-2026-109619